Read more ->
 8 Min
Encryption is fundamental for internet security and elliptic curve cryptography (ECC) will become the next standard in the industry. Find out why and keep up to date with the latest security improvements.

From internet surfing to data transfers, banking transactions and messaging apps, the web is an ocean of sensitive or personal data. Security experts have been working hard to create technology capable of thwarting hackers. Computer science has adopted encryption to secure information by mathematically encoding it. Behind its functioning are algorithms that developed over a thousand years of progress.
So why do we need encryption? The immensely widespread and ever-expanding use of the global internet requires us to adopt very secure solutions. While RSA encryption, based on private and public keys, has been the standard for decades, elliptic curve cryptography now offers the same security with much shorter keys. Neither RSA nor ECC can withstand a future large-scale quantum computer, however, which is why NIST approved its first post-quantum cryptography standards in August 2024.
Today, elliptic curve cryptography (ECC) is regarded as one of the most robust types of encryption and has become a valuable ally for cybersecurity. We invite you to read this article for a more detailed introduction to ECC encryption and to discover why it has become a standard part of internet security, for example as a mandatory key exchange method in TLS 1.3.
Nowadays, encryption is the standard measure to protect communications in the digital ecosystem. Its extensive protective shield spans from HTTPS connections to securing information transmitted in data centers.
Encryption belongs to the ancient field of cryptography and is a process for encoding information. It has been used for centuries to convert the original message into unintelligible ciphertext that only the authorized and intended recipients can decipher. Both then and now, the aim was to prevent unauthorized parties from accessing critical information or communications.
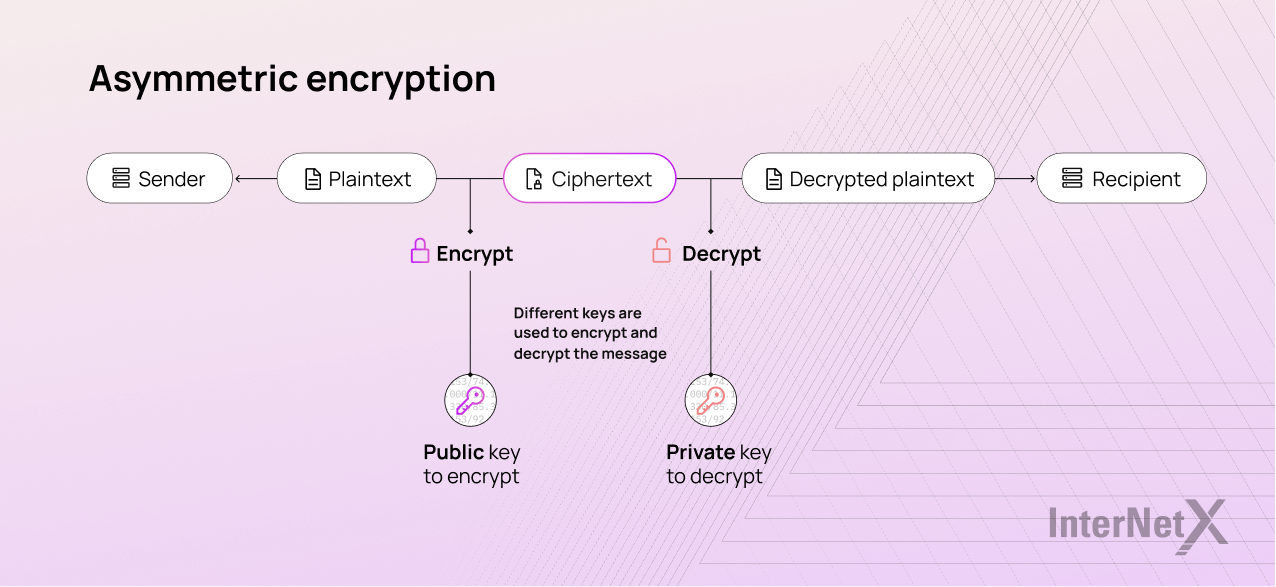
We can distinguish between two main widespread forms of encryption today, namely symmetric and asymmetric encryption. The main difference lies in whether the same key is used for encryption and decryption.
When the sender and the recipient share only one single key, we speak of symmetric key cryptography. The single key is used to both hide and unlock the message. Compared to other types of encryption, it is quick and easy.
Well-known examples of symmetric encryption include:
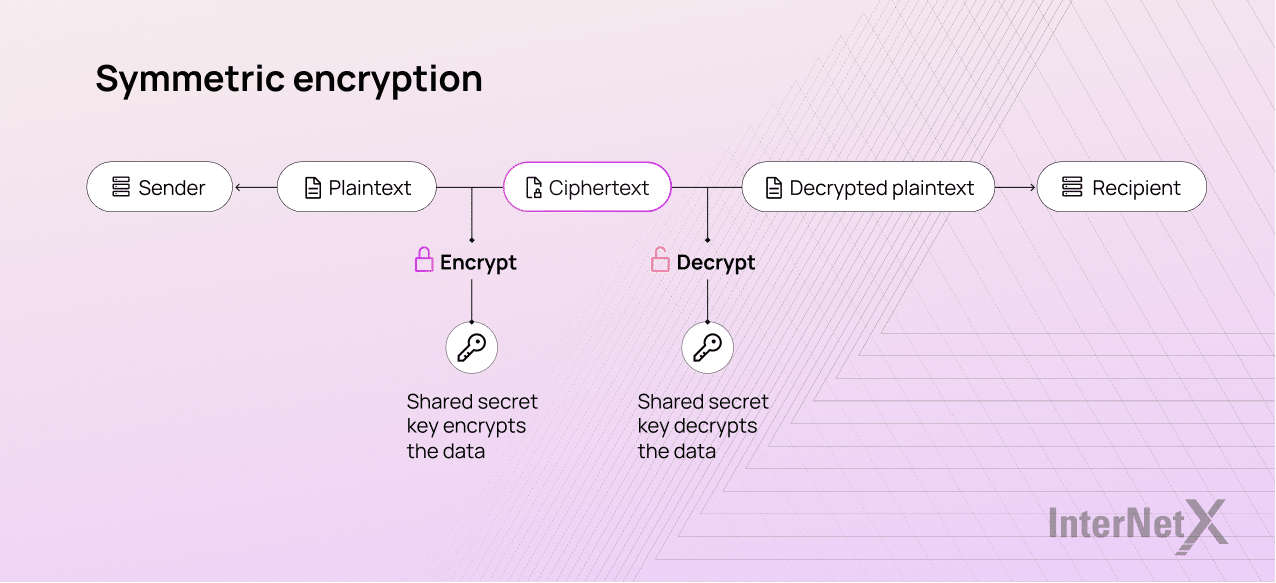
Asymmetric algorithms use two interdependent keys, a public and a private key, one to encrypt data and one to decrypt it. The recipient knows both keys, the private and the public one. He should never share the private key that he needs for decryption. The public key is used by the sender to encrypt the message. One of the most common uses of asymmetric cryptography is to digitally sign a certificate in order to verify the authenticity of a document or the integrity of a message.
Examples of asymmetric encryption include:
Secure Sockets Layer (SSL) and its successor, Transport Layer Security (TLS), are encryption protocols used for protecting data over the internet or a computer network. SSL 3.0 was deprecated in 2015, so today's TLS/SSL certificates are in fact used with TLS. Having a TLS/SSL certificate on your domain has become the standard for most web browsers or servers. These two types of encryption can follow the symmetric and asymmetric models with different goals to protect the internet. While symmetric encryption protects data exchange within a session, asymmetric encryption establishes secure communication between the client and server.
The concept of elliptic curve cryptography (ECC) is not new, at least in mathematics. It was proposed in the mid ’80s by Victor Miller of IBM and Neal Koblitz of the University of Washington.
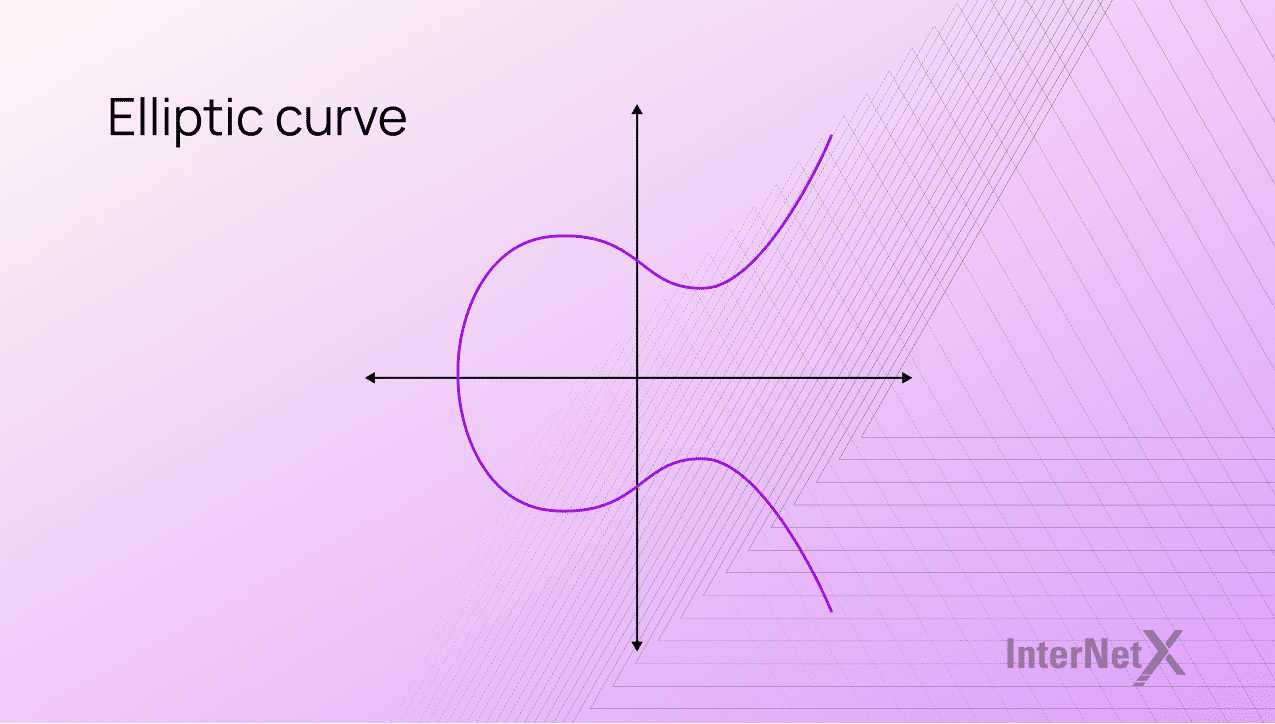
Elliptic curve encryption algorithms started enjoying widespread use around 2004-2005. ECC has established itself in computer science as a more robust alternative to public-key systems like RSA, DSA and Diffie-Hellman. One of the best-known uses is probably the Elliptic Curve Digital Signature Algorithm (ECDSA). ECC is a form of public-key cryptography or asymmetric encryption, freely distributed with a private key and a public one.
ECC relies on how hard it is to solve the discrete logarithm problem on an elliptic curve, while RSA relies on how hard it is to factor very large numbers. The larger the curve, the higher the security. Because the elliptic curve problem is much harder to solve at the same key length, ECC can use shorter keys, which improves the performance of digital certificates.
The National Institute of Standards and Technology (NIST) specifies ECC in its Federal Information Processing Standard FIPS 186-5 and in SP 800-186, both published in February 2023, and the National Security Agency has also approved it. Adopting this strong cryptography will help us migrate to higher security strengths.
ECC has many groups of algorithms for digital signature, encryption and key agreement. The most well-known signature scheme that uses elliptic curves is the Elliptic Curve Digital Signature Algorithm (ECDSA). It is an alternative encryption system to the classic Digital Signature Algorithm (DSA) system using elliptic curves. It was proposed for the first time by Scott Vanstone.
ECDSA is widely used to sign software, and Bitcoin and other blockchains use ECDSA key pairs to sign cryptocurrency transactions. Thanks to the shorter key lengths and its high efficiency, it has become quite popular.
As is commonplace for elliptic curve cryptography, the bit size of the key needed by ECDSA is approximately twice the security level in bits. Therefore, a security level of 128 bits requires a key size of about 256 bits, while DSA and RSA need 3,072-bit keys for the same security level. This results in faster algorithms and improves performance.
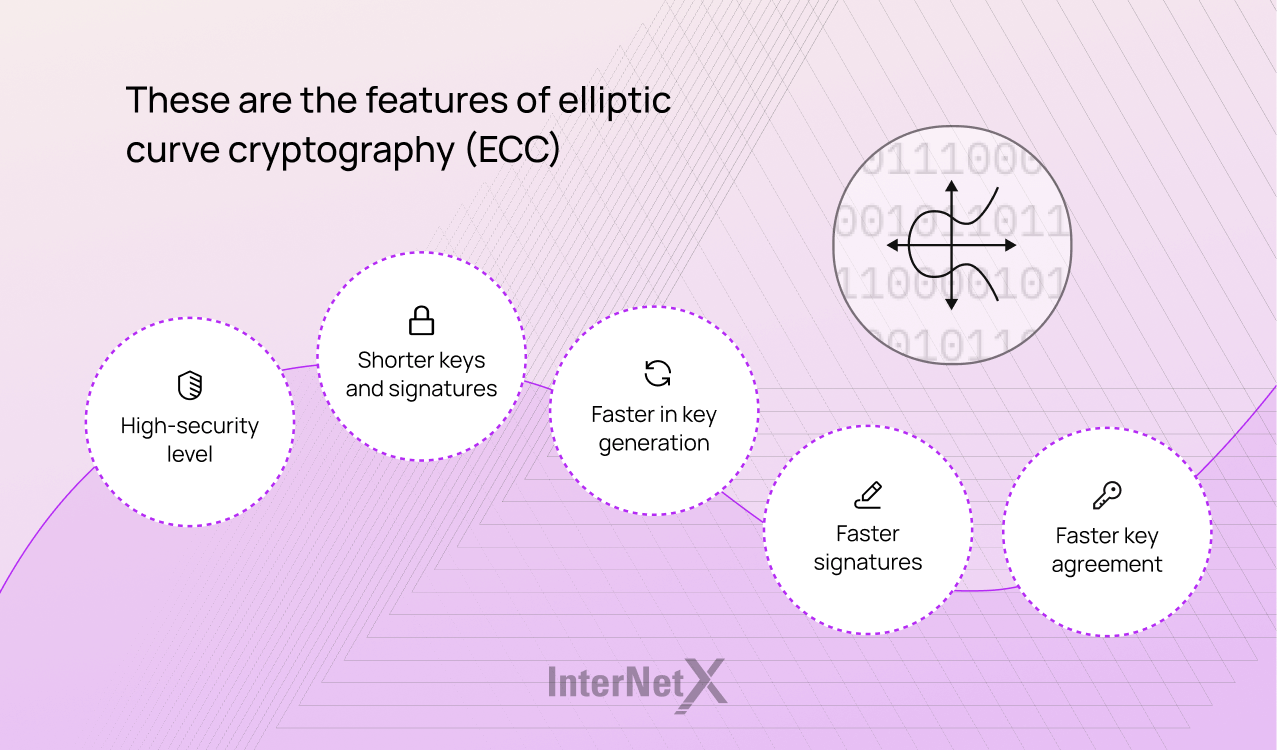
ECC has been used successfully in internet protocols for many years, for example in TLS since 2006, proving to be a reliable and potent solution. This new encryption method has the right features for the digital world with its extensive data volume exchange. It can guarantee a higher level of security, better performance and shorter keys for increased speed.
The shorter keys require less computing power, which means secure and faster connections. For example, a 256-bit ECC key provides the same security level as a 3072-bit RSA key. This element is particularly crucial in a world where users predominantly browse the web with mobile devices such as smartphones and tablets.
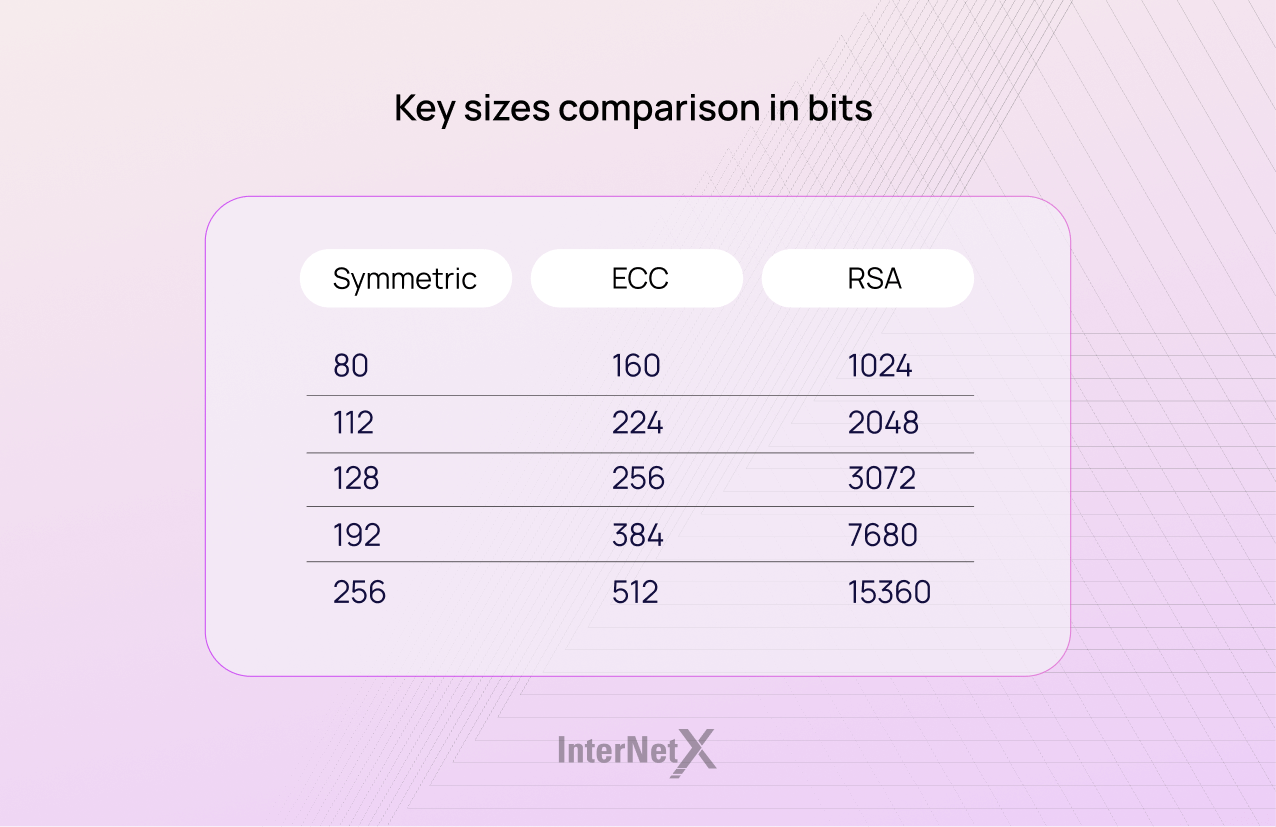
Digital certificates with ECC have more advantages. They are generally lighter, faster and more secure than RSA. Keys in RSA are massive, almost unwieldy. The current standard is 2,048 bits, though some go up to 4,096 bits. Let’s take a detailed look at the advantages of ECC.
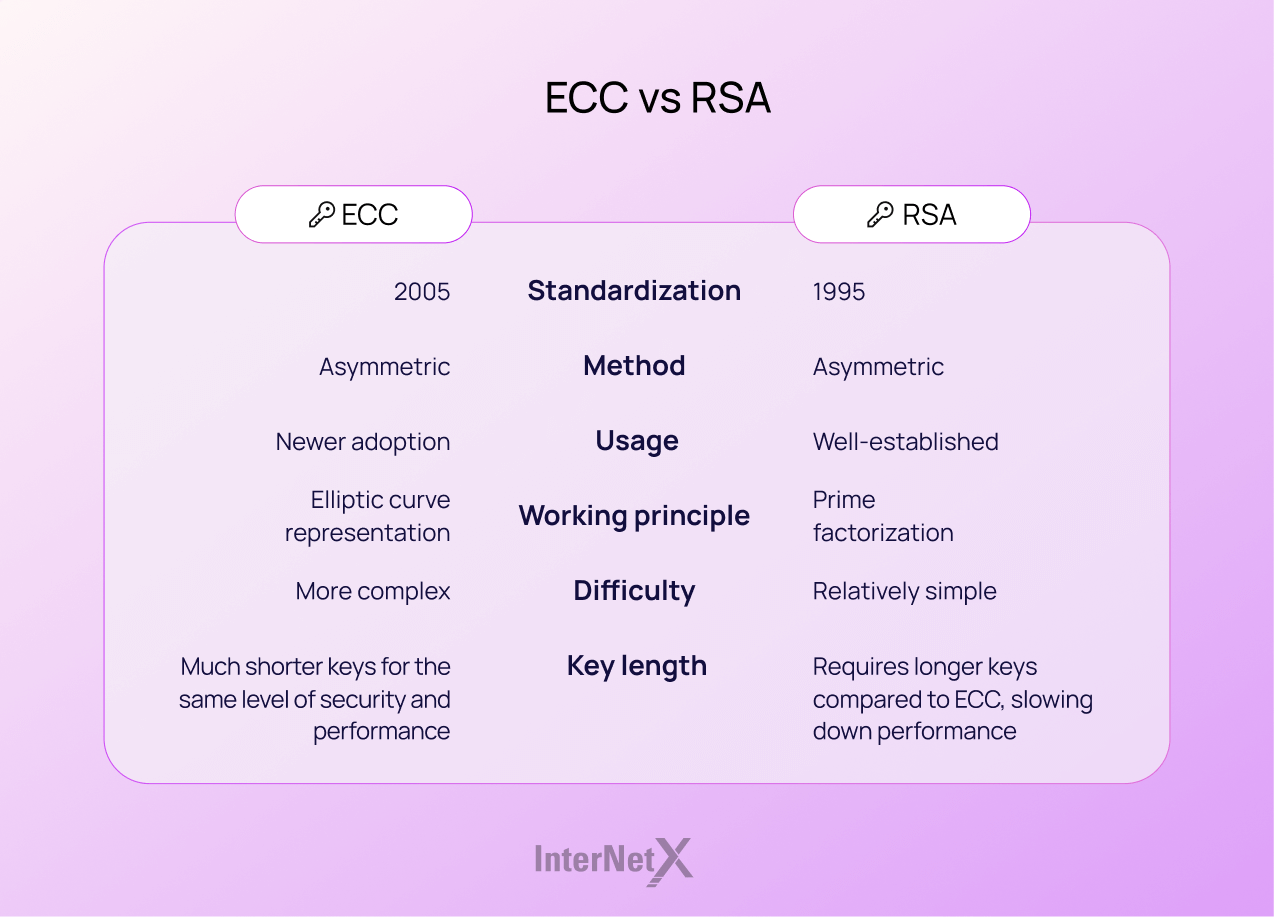
Although ECC provides an excellent alternative to the traditional public-key scheme, it has some disadvantages compared with RSA encryption.
ECC is more complex and could be challenging to set up securely. This increases the likelihood of implementation errors, reducing the algorithm’s security. Understanding the EC-based protocol requires a considerable wealth of algebraic and geometric skills.
What is the security level offered by ECC? Ways and means to attack ECC and exploit its vulnerabilities do exist. For example, side-channel or twist-security attacks can invalidate the safety of private keys. Proper countermeasures, parameter validation and appropriate curve choices can mitigate these threats. Although not 100% secure, ECC still remains an extremely effective and highly secure method.
Elliptic curve cryptography is one of the most efficient public-key systems in wide use today. TLS/SSL certificates with ECC are ideal to scale up your business. They perform at their best for scenarios in which the server load is critical and website or app users are compatible with ECC keys.
At InterNetX, you can opt for this technology for all your web, mobile and desktop applications services.
More about digital certificate with ECC


No spam.
Just quality content.